iFLEX at AAPEX | Shops Must Be Vigilant Against Cyber Attacks

Ransomware, phishing emails, and other spyware threaten the security of automotive aftermarket businesses and their customers, says Jason Kerr, a cybersecurity expert who presented at iFLEX at AAPEX.

Key Highlights


In today’s digital world, cybersecurity is a critical concern for businesses of all sizes. Companies—regardless of their market—rely more heavily on technology than ever before.  


They use it to store information, communicate with customers, and carry out daily operations. As businesses come to rely more heavily on technology, the risk of cyber threats becomes increasingly more pertinent.  


“Cyber threats don’t discriminate,” said Jason Kerr, a home office account executive at ARMS. “Attacks happen to all sizes and types of businesses regardless of industry, expertise, and location. The best way to tackle this growing risk is to proactively plan for a Cyber Security Event versus being reactive.” 


These attacks can have a detrimental effect on your company.  


“They can result in financial loss to even shutting your business doors for good,” Kerr said. “The best way to combat this: Create a risk management plan outlining what type of information is at stake, current security practices, what to do in the event of a cybersecurity attack, and safety training.” 


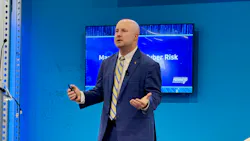
To help the automotive aftermarket better understand and address these growing threats, Kerr presented a seminar on managing cyber risk at the iFLEX at AAPEX.  


Managing Cyber Risk 


During this session, Kerr covered common cyber threats, what happens after an attack, and practical steps businesses can take to reduce risk. 


“Cyber risk management is something all businesses should not only be paying attention to, but also implementing in their workplaces as soon as possible,” Kerr said.  


According to Kerr, the most common cyber risks that businesses tend to overlook are: 


Business email compromise: Phishing events targeting payments, transactions, and personal protective information, often involving the use of ransomware, which renders targets’ devices unusable until a monetary ransom is paid to the attacker. 


Spyware: A type of malicious code software installed unknowingly to gather sensitive information. 


Trojan horse: A computer program that appears to be a useful function, but has a hidden malicious function that evades security mechanisms which can exploit legitimate authorizations of a system entity. 


These risks can develop into cyber attacks instantaneously and result in high profit loss for the company. Kerr offered the following examples, removing company and personal information: 


Example #1: A phishing email launched a ransomware attack that locked the business’s computer system/network.  


IT restored the system via backups and data recreation, which eliminated the need to pay the ransom. But because Forensic IT confirmed a data breach, the business was required to notify impacted clients and provide credit-monitoring services. The business hired a PR firm to manage its social media following the breach. The incident resulted in lost data and extra expenses related to regulatory compliance. Total loss: $178,491.  


Example #2: A ransomware attack released through a phishing email locked up the business’s POS system. It encrypted their network and caused significant loss of business income. A forensic IT and legal review determined that the ransom should be paid to restore the business’ data and operations. Total loss: $377,951.  


Example #3: A business IT provider uncovered encrypted services and a ransom note. A forensic IT review confirmed a breach of the clients’ credit card data. The business lost income and incurred data and system restoration costs. No ransom paid. Total loss: $284,059.  


Proactive Planning 


The information provided above demonstrates the potentially significant financial impact of a cyberattack. For automotive aftermarket businesses, proactive planning can make a critical difference in minimizing disruptions, managing expenses, and protecting customer information. 


Kerr’s Managing Cyber Risk seminar at the iFLEX booth offered attendees practical insights into cyber risk and developing strategies to help protect their businesses. 


“Creation of a business-specific risk management plan accompanied by the right cyber insurance coverage can help provide you with protection against the unexpected,” Kerr said. 


By taking preventative steps, the automotive aftermarket can be better prepared to navigate today’s evolving cyber threat lan
 

In today’s digital world, cybersecurity is a critical concern for businesses of all sizes. Companies—regardless of their market—rely more heavily on technology than ever before.  

They use it to store information, communicate with customers, and carry out daily operations. As businesses come to rely more heavily on technology, the risk of cyber threats becomes increasingly more pertinent.  

“Cyber threats don’t discriminate,” said Jason Kerr, a home office account executive at ARMS. “Attacks happen to all sizes and types of businesses regardless of industry, expertise, and location. The best way to tackle this growing risk is to proactively plan for a Cyber Security Event versus being reactive.” 

These attacks can have a detrimental effect on your company.  

“They can result in financial loss to even shutting your business doors for good,” Kerr said. “The best way to combat this: Create a risk management plan outlining what type of information is at stake, current security practices, what to do in the event of a cybersecurity attack, and safety training.” 

To help the automotive aftermarket better understand and address these growing threats, Kerr presented a seminar on managing cyber risk at the iFLEX at AAPEX.  

Managing Cyber Risk 

During this session, Kerr covered common cyber threats, what happens after an attack, and practical steps businesses can take to reduce risk. 

“Cyber risk management is something all businesses should not only be paying attention to, but also implementing in their workplaces as soon as possible,” Kerr said.  

According to Kerr, the most common cyber risks that businesses tend to overlook are: 

Business email compromise: Phishing events targeting payments, transactions, and personal protective information, often involving the use of ransomware, which renders targets’ devices unusable until a monetary ransom is paid to the attacker. 

Spyware: A type of malicious code software installed unknowingly to gather sensitive information. 

Trojan horse: A computer program that appears to be a useful function, but has a hidden malicious function that evades security mechanisms which can exploit legitimate authorizations of a system entity. 

These risks can develop into cyber attacks instantaneously and result in high profit loss for the company. Kerr offered the following examples, removing company and personal information: 

Example #1: A phishing email launched a ransomware attack that locked the business’s computer system/network.  

IT restored the system via backups and data recreation, which eliminated the need to pay the ransom. But because Forensic IT confirmed a data breach, the business was required to notify impacted clients and provide credit-monitoring services. The business hired a PR firm to manage its social media following the breach. The incident resulted in lost data and extra expenses related to regulatory compliance. Total loss: $178,491.  

Example #2: A ransomware attack released through a phishing email locked up the business’s POS system. It encrypted their network and caused significant loss of business income. A forensic IT and legal review determined that the ransom should be paid to restore the business’ data and operations. Total loss: $377,951.  

Example #3: A business IT provider uncovered encrypted services and a ransom note. A forensic IT review confirmed a breach of the clients’ credit card data. The business lost income and incurred data and system restoration costs. No ransom paid. Total loss: $284,059.  

Proactive Planning 

The information provided above demonstrates the potentially significant financial impact of a cyberattack. For automotive aftermarket businesses, proactive planning can make a critical difference in minimizing disruptions, managing expenses, and protecting customer information. 

Kerr’s Managing Cyber Risk seminar at the iFLEX booth offered attendees practical insights into cyber risk and developing strategies to help protect their businesses. 

“Creation of a business-specific risk management plan accompanied by the right cyber insurance coverage can help provide you with protection against the unexpected,” Kerr said. 

By taking preventative steps, the automotive aftermarket can be better prepared to navigate today’s evolving cyber threat landscape.

About the Author

Sign up for our eNewsletters
Get the latest news and updates